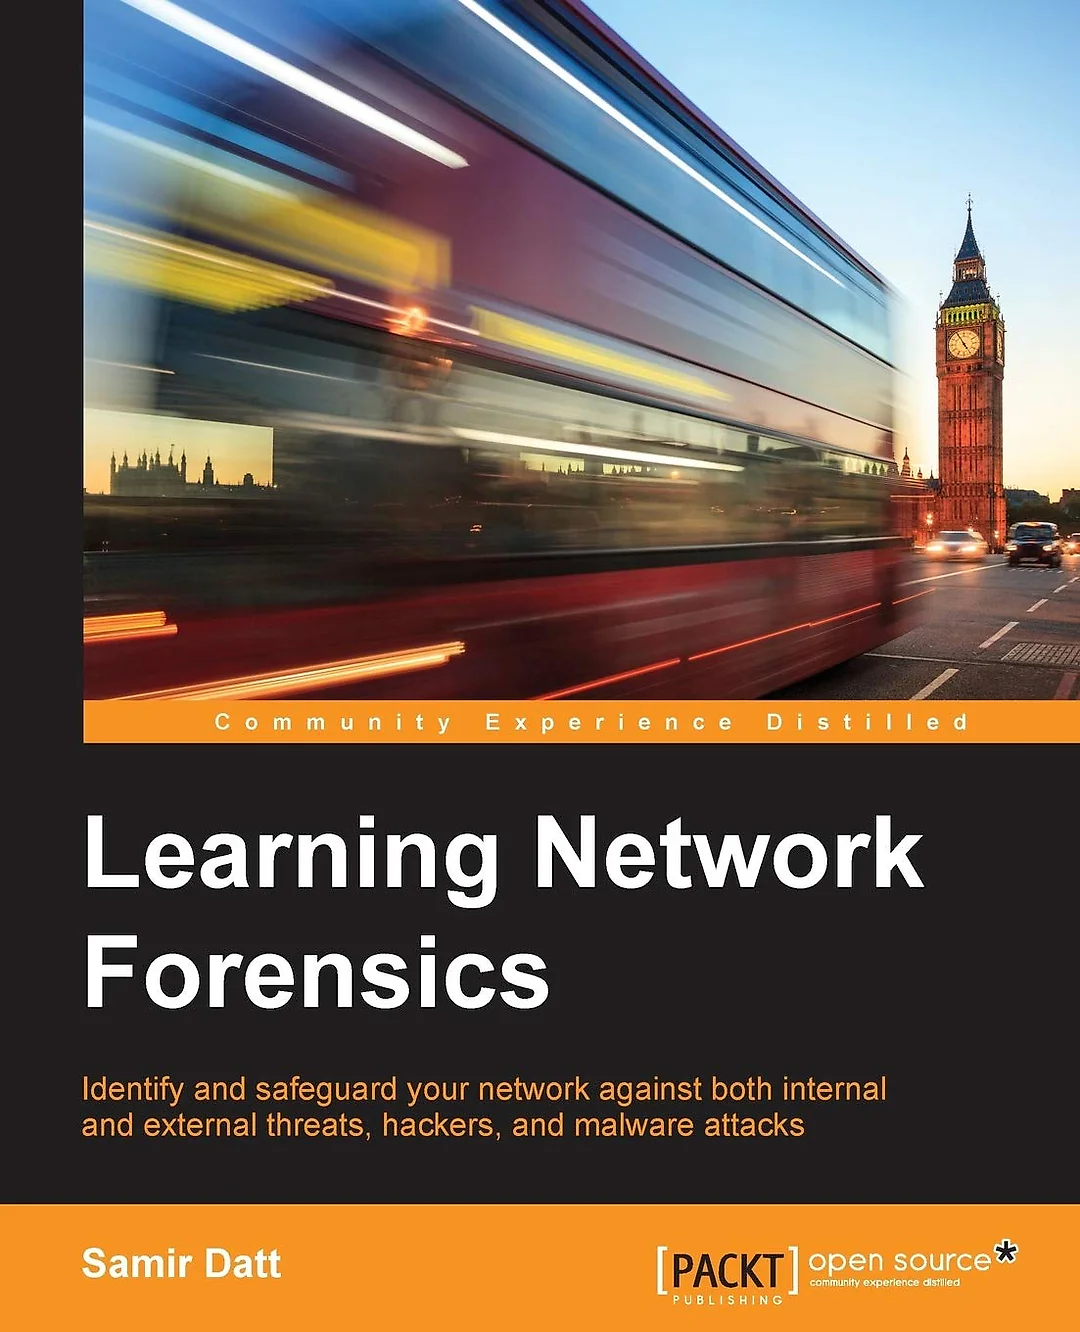
Learning Network Forensics
In stock
Learning Network Forensics
$55.00
Identify and safeguard your network against both internal and external threats, hackers, and malware attacks About This Book
- Lay your hands on physical and virtual evidence to understand the sort of crime committed by capturing and analyzing network traffic
- Connect the dots by understanding web proxies, firewalls, and routers to close in on your suspect
- A hands-on guide to help you solve your case with malware forensic methods and network behaviors
Who This Book Is For
If you are a network administrator, system administrator, information security, or forensics professional and wish to learn network forensic to track the intrusions through network-based evidence, then this book is for you.
Basic knowledge of Linux and networking concepts is expected.
What You Will Learn
- Understand Internetworking, sources of network-based evidence and other basic technical fundamentals, including the tools that will be used throughout the book
- Acquire evidence using traffic acquisition software and know how to manage and handle the evidence
- Perform packet analysis by capturing and collecting data, along with content analysis
- Locate wireless devices, as well as capturing and analyzing wireless traffic data packets
- Implement protocol analysis and content matching; acquire evidence from NIDS/NIPS
- Act upon the data and evidence gathered by being able to connect the dots and draw links between various events
- Apply logging and interfaces, along with analyzing web proxies and understanding encrypted web traffic
- Use IOCs (Indicators of Compromise) and build real-world forensic solutions, dealing with malware
In Detail We live in a highly networked world. Every digital device - phone, tablet, or computer is connected to each other, in one way or another. In this new age of connected networks, there is network crime. Network forensics is the brave new frontier of digital investigation and information security professionals to extend their abilities to catch miscreants on the network. The book starts with an introduction to the world of network forensics and investigations.
You will begin by getting an understanding of how to gather both physical and virtual evidence, intercepting and analyzing network data, wireless data packets, investigating intrusions, and so on. You will further explore the technology, tools, and investigating methods using malware forensics, network tunneling, and behaviors. By the end of the book, you will gain a complete understanding of how to successfully close a case. Style and approach An easy-to-follow book filled with real-world case studies and applications.
Each topic is explained along with all the practical tools and software needed, allowing the reader to use a completely hands-on approach.
Book Details
- Author: Samir Datt
- Publisher: Packt Publishing
- eBook ISBN: 9781785282126, 1785282123
- Print ISBN: 9781782174905, 1782174907
Product Details
You May Also Like
View all →
Advances in Computer Science and Information Technology: First International Conference on Computer Science and Information Technology, CCSIT 2011, Bangalore, India, January 2-4, 2011. Proceedings, Part I
Designing Democracy Re-education and the America Houses (19451961)- The American Information Centers and their Involvement in Democratic: Re-education in Western Germany and West Berlin from 1945 to 1961

Advances in Neuroergonomics and Cognitive Engineering: Proceedings of the AHFE 2016 International Conference on Neuroergonomics and Cognitive Engineering, July 27-31, 2016, Walt Disney World®, Florida, USA